JWT + Role-Based Access in Spring Security: Refresh Tokens Without the Footguns
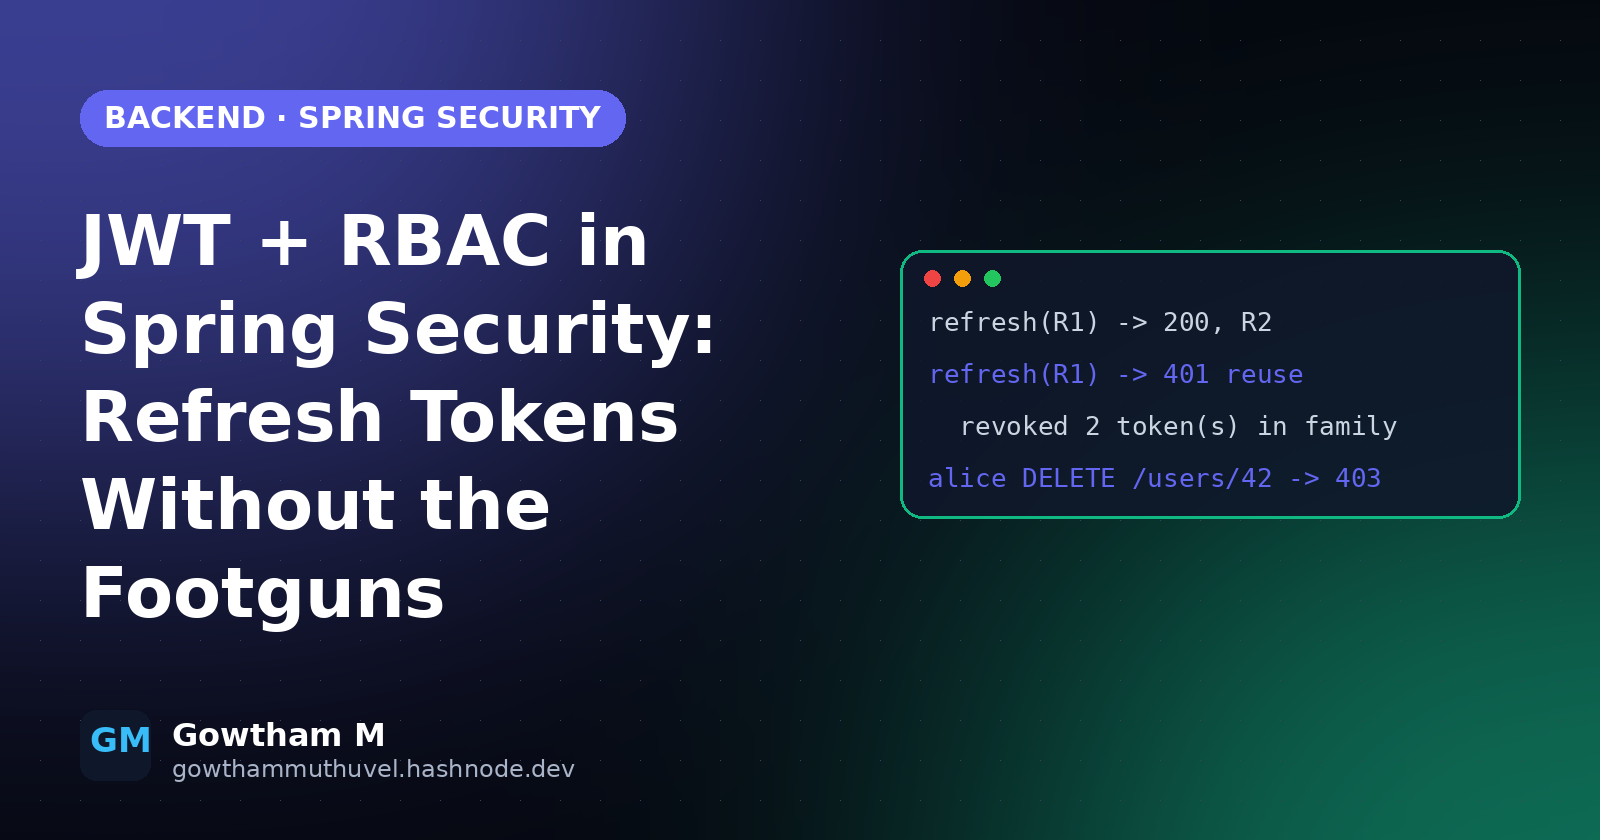
Rotation with reuse detection, ROLE_ vs SCOPE_ mapping, and the permitAll() trap, all tested on Spring Boot 4.1.2. Replaying an old refresh token revoked 2 tokens and killed the session.